QuantumLock™ Module
QCOS Quantum Isolation™
An isolation policy for multi-tenant execution on shared quantum hardware. In our Monte Carlo simulation, cross-tenant leakage falls to statistically indistinguishable from random guessing. It has not been validated on a physical device, and QCOS offers no QPU access today.
- Powered by QuantumLock™
- Sealed evidence bundles
- NDA available on request
Opening film: MrColo on Pexels (Pexels License), cropped and graded. It shows generic server hardware, not a SoftQuantus system or a quantum processor.
- Baseline Attack AccuracyWithout isolation (simulation)
- 99.9%
- With QCOS EXTREMESimulation result: indistinguishable from random
- 51.4%
- Bits Mutual Information99.4% reduction from baseline (simulation)
- 0.003
- Adversarial AdvantageMaximum across 4 classifier families (simulation)
- 1.4 pp
The problem: multi-tenant QPUs create a physical side-channel
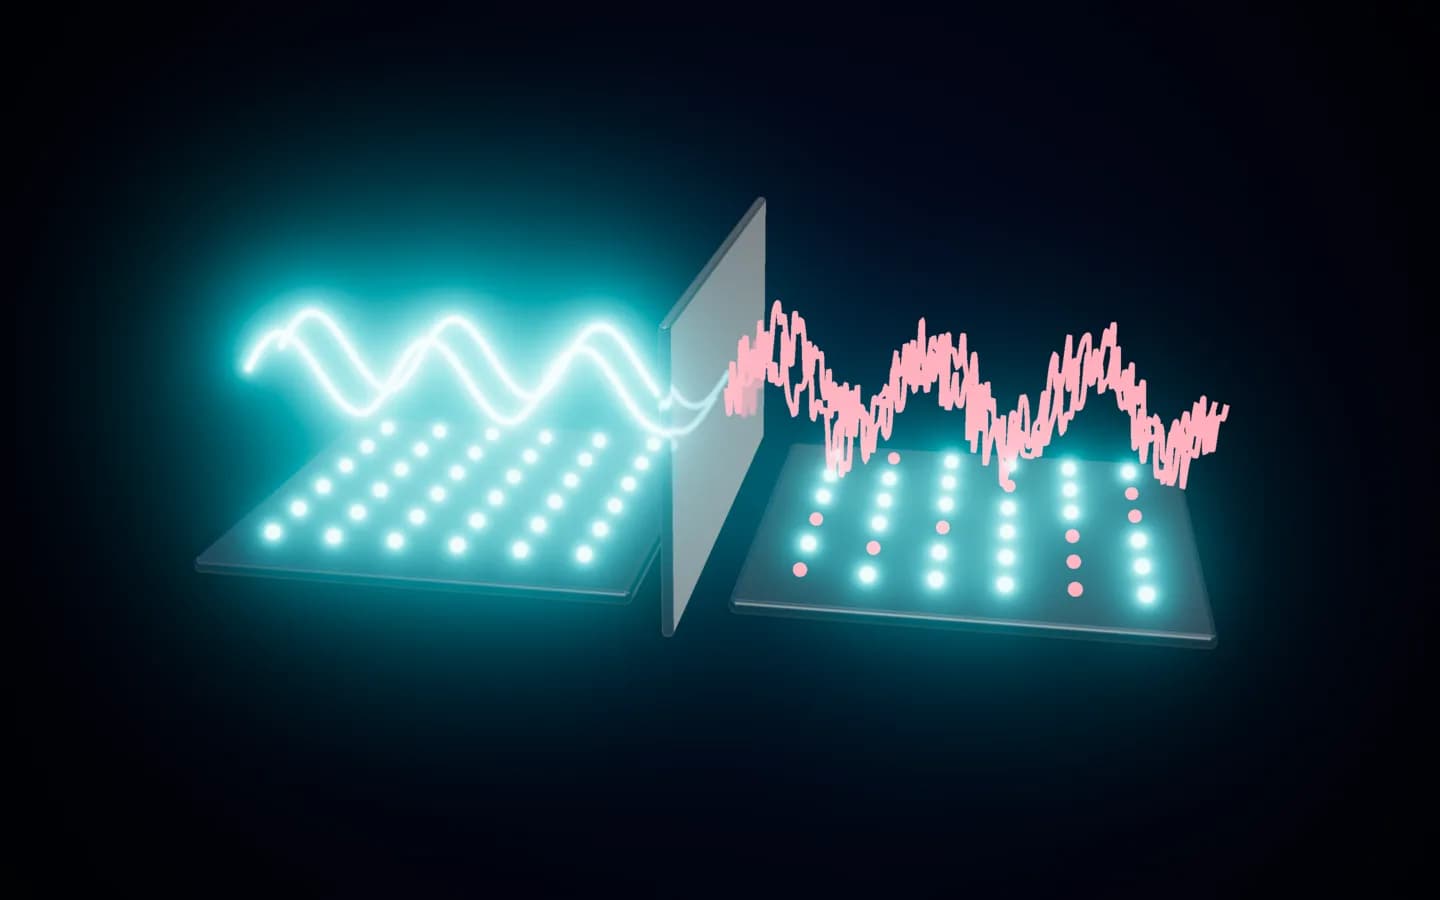
Cloud quantum computing is inherently shared. When different tenants execute on neighboring qubits, crosstalk and timing correlations can create a measurable side-channel. A co-tenant can attempt to infer the class of a victim workload using sensor circuits and statistical learning.
- 01
IP Leakage Risk
Algorithms, model structure, and circuit families can be inferred by malicious co-tenants. - 02
Vendor Risk
Tenant isolation is often not quantified in provider documentation. - 03
Compliance Risk
Hard to audit, hard to prove non-disclosure. Regulators require quantified security evidence.
Use case
How it works
A layered isolation strategy targeting the physical leakage channel
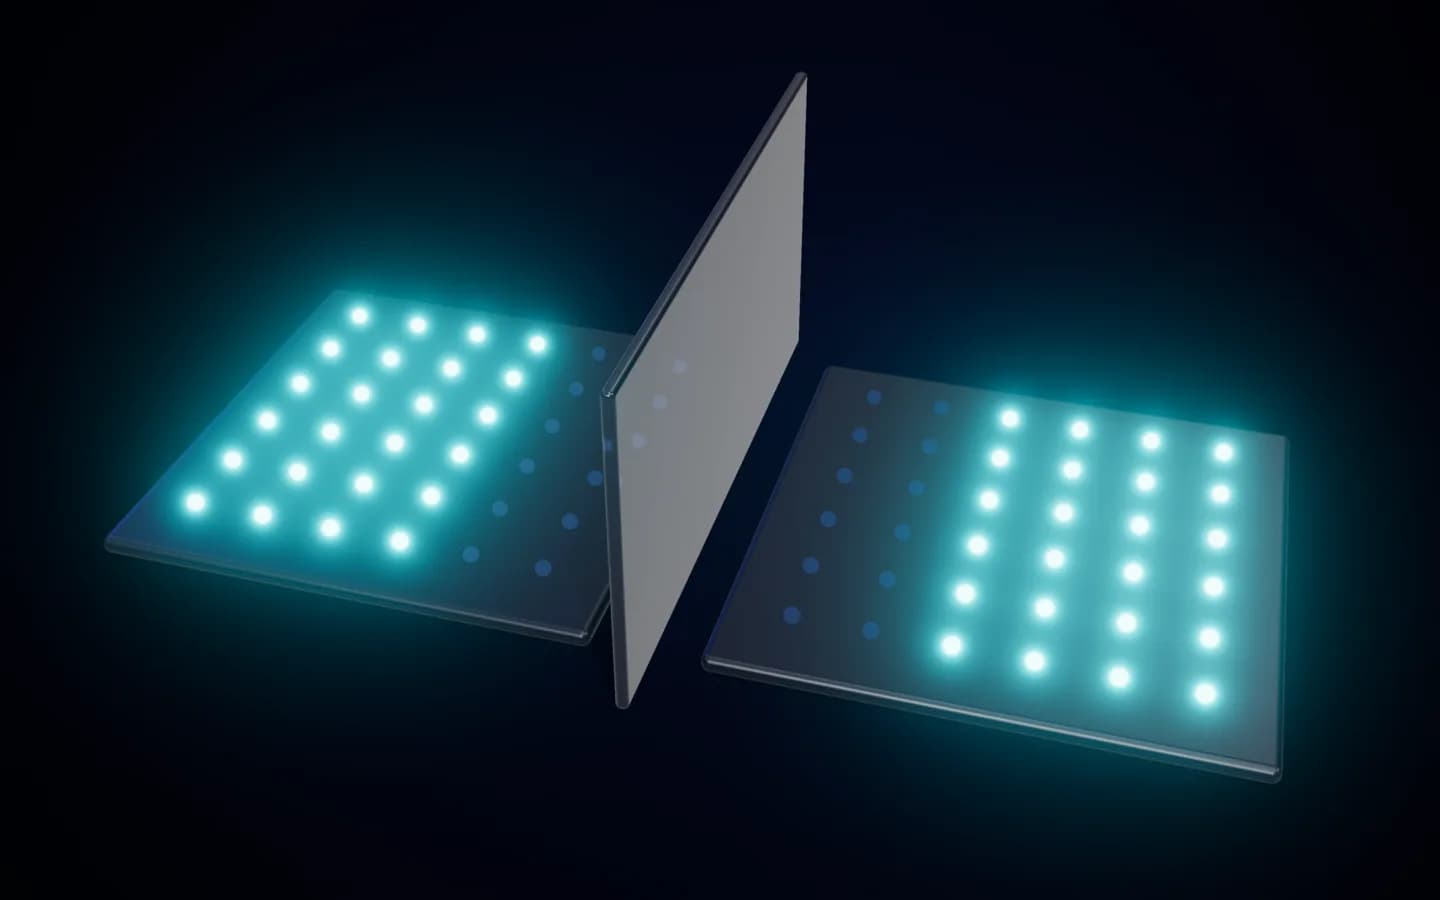
Topology-aware placement enforces physical distance between tenants to attenuate electromagnetic coupling.
Qubit mapping changes per execution to prevent cross-run statistical accumulation attacks.
Randomized timing and reset barriers reduce synchronization and drift exploitation between tenants.
Independent decoy workloads reduce side-channel SNR. Generated independently of victim structure, with second-order impact evaluated in simulation.
What QCOS Quantum Isolation delivers
Simulation results with auditable evidence, bounded by an explicit threat model.
{
  "isolation_level": "EXTREME",
  "max_attacker_accuracy": 0.514,
  "wilson_95_ci": [0.483, 0.545],
  "contains_random": true,
  "binomial_test_p": 0.38,
  "mutual_information_bits": 0.003,
  "adversarial_advantage_pp": 1.4,
  "verdict": "INDISTINGUISHABLE_FROM_RANDOM"
}- 01
Quantified in Simulation
In a Monte Carlo simulation of the threat model, attack success falls to random guessing: the Wilson 95% CI includes 50% and the exact binomial test fails to reject p = 0.5. - 02
Auditable Evidence
Tamper-evident Isolation Evidence Bundle per run. Export as JSON and PDF, sealed with a SHA-256 content hash, for security reviews. - 03
Controlled Overhead
Security-utility tradeoffs are explicit. The simulation model assumes 11% qubit overhead, 15% throughput impact and <0.5% fidelity loss; none of these is measured on hardware. - 04
Physical Isolation Model
A layered policy modelled in simulation: topological buffering, layout randomization, temporal decorrelation and decoy injection. Not yet applied to a real multi-tenant QPU.
Isolation tiers
Choose the right balance of security and overhead for your workload
ENTERPRISE
STANDARD
Logical isolation
- Scheduler-level separation
- Basic buffer policy
ENTERPRISE
HIGH
Buffer + temporal gap
- 1-qubit buffer zone
- 100μs scheduling gap
- Reset barriers
ENTERPRISE
MAXIMUM
Verified reset barriers
- 2-qubit buffer zone
- 1ms scheduling gap
- Post-reset verification
DEFENSE
EXTREME
Largest simulated reduction
- 3-qubit dynamic buffer
- 5ms temporal gap
- Per-job layout randomization
- Active decoy injection
- Tamper-evident evidence bundle
Who this is for
Built for regulated industries and security-conscious organizations
Financial Services
Government & Defense
Pharma & Life Sciences
Hardware Vendors
Cloud Platforms
Industrial R&D
What we don't claim
Built for procurement-grade credibility. Our claims are bounded by an explicit threat model and measurable metrics.
- No claim of universal physical limits across all architectures
- No claim of "zero leakage" — claims are bounded by explicit threat model
- Metrics come from a Monte Carlo simulation, summarised with Wilson confidence intervals and exact binomial tests
- Four classifier families were tried in simulation; adaptive adversaries on real hardware have not been tested
- Overhead figures are model assumptions, not hardware measurements
- No real multi-tenant QPU has been tested, and QCOS does not offer QPU access today
Request access
Get a security review package or a simulation-based pilot design for your target QPU topology.
Contact: info@softquantus.comNDA available on request